
How merchants get started
01
Tell us about your business — sector, markets, volumes
02
Sign the technology licence and receive API credentials and a test environment
03
Generate your own signing key, integrate and go live

One licence, one integration
Software you run with your own key, for customers paying from a wallet they control.
SpendLayer Direct
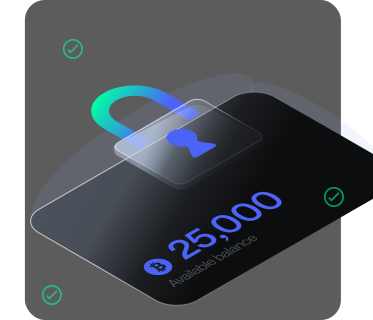
Your customer chooses SpendLayer Direct at your checkout and approves a mandate on the SpendLayer consent screen, from their own wallet. The mandate is between them and you, with a defined amount, frequency and limit. You validate and sign each collection, and value moves on-chain straight to your wallet — never through ours.
Recurring, natively
Subscriptions and instalments run under the customer’s mandate, without them re-authorising each time. The limits they set are enforced on-chain.

Auditable end to end
Every authorisation and collection is a public on-chain event, verifiable without access to our systems.

How
Direct
works at checkout
Your customer approves on the SpendLayer consent screen, never on your checkout, so no wallet credential ever passes through your systems. Every collection then needs two signatures: the customer’s mandate and your own.

Customer approves a mandate on the SpendLayer consent screen, from their own wallet
The mandate is recorded on-chain — amount, frequency, duration, ceiling
We prepare each collection; you validate it against your own records and sign it with your key
Value moves on-chain in a single transaction, and the transfer is final


Monthly
Subscription
-12.50 USDC

Recurring
Top-up
-9.99 USDC

Instalment
Plan
-29.00 USDC

Why on-chain matters to you
Flows your partners can verify for themselves, rather than taking anyone’s word for them
Independently auditable
Auditors, banks and partners can verify flows on-chain, not by asking us for a report.
Rules in code
Mandate limits are enforced on-chain and deterministic. A collection outside them is rejected.
Final transfers
Transfers are final on-chain. No dispute path, and no clawback months later.
Customers cards miss
Reaches wallet-native customers you cannot serve through a card checkout.
Two calls and a signature
Create a request from your server, send the customer to the hosted consent screen we return, and fulfil the order when the completion webhook arrives. Authentication is an API key plus an HMAC-SHA256 signature over the request body.
Distribute SpendLayer technology
Merchants can integrate SpendLayer Direct themselves, and many prefer not to. If you already serve merchants — as an integrator, a platform, an agency or a payments business — you can become an appointed distributor for your region and license the technology to the merchants you bring.
Frequently asked questions
Still have questions?
Tell us about your business. Once the technology licence is signed we issue credentials and a test environment.
No. SpendLayer licenses software. We never hold, receive or transmit your funds or your customers’ funds, we hold no key to any wallet in the flow, and we cannot initiate, block or reverse a transfer. Every collection is authorised by your customer’s mandate and by your own signature.
Because you run the technology yourself, any licence, registration or compliance obligation that applies to your business remains yours.
Yes. SpendLayer Direct can be integrated straight into your own checkout. The core integration is two API calls — one to create a request and return the consent link, one to follow its status — with webhooks if you would rather not poll. You then validate and sign each collection with your own key.
Tell us about your business. Once the technology licence is signed we issue API credentials and a test environment. The full reference is in our integration docs.
Every SpendLayer wallet is linked to a unique 16-digit authorisation code. Your customer uses it on the SpendLayer consent screen to identify their wallet and approve a mandate from it.
The code is an access credential, so it is entered only on that screen and never on yours, and it never reaches your systems. It does not expose their private key, and it gives SpendLayer no ability to move anything. Value moves only within the mandate the customer approved, and only under a transaction you sign.
Collection stops from that point. Revocation is unilateral and takes effect on-chain, so you will not be able to collect further instalments under that mandate, and there is no retry path.
In practice it works like a cancelled subscription: you keep everything already collected, and you handle the cancellation in your own billing logic. Every revocation is an on-chain event, so it is visible to your systems immediately rather than surfacing later as a failed charge.
Yes. Your signing key is generated in your own browser the first time you sign in. It never reaches SpendLayer, is never stored on our systems, and we cannot recover, reset or restore it.
Back it up before you go live. If you lose it you lose the ability to sign collections from your wallet, and nobody can restore it for you.
Yes. You can originate and submit any collection a mandate permits yourself, without SpendLayer preparing anything. Our transaction preparation is a convenience, not a dependency.
The full merchant integration reference is in our integration docs — endpoints, request signing, the status lifecycle and webhook payloads, with worked Node.js examples.
It covers the hosted consent flow. Recurring collection under a mandate is handled separately, so raise it with your integration contact if you need it.
Availability varies by product and jurisdiction, and sanctioned jurisdictions are excluded throughout. Tell us where you operate and we will confirm what is available to you.
